
The email arrives with a subject line like We’ve detected unusual activity, or you read in the news that a service you signed up for years ago has been hacked. Most people do one of two things: panic and change everything, or shrug and do nothing. Neither is ideal. A calm, ordered data breach response takes less than an hour and covers most of the risk.
First, find out what was taken
Breaches differ enormously. Exposed email addresses are an annoyance. Exposed passwords are more serious, and exposed financial or identity details can have lasting consequences. Read the company’s notice carefully and look for what categories of data were involved, whether passwords were stored in hashed form, and what it advises. Be cautious about where you read it: attackers send fake breach notices to steal credentials. Go to the company’s site by typing the address yourself, not through a link in the email.
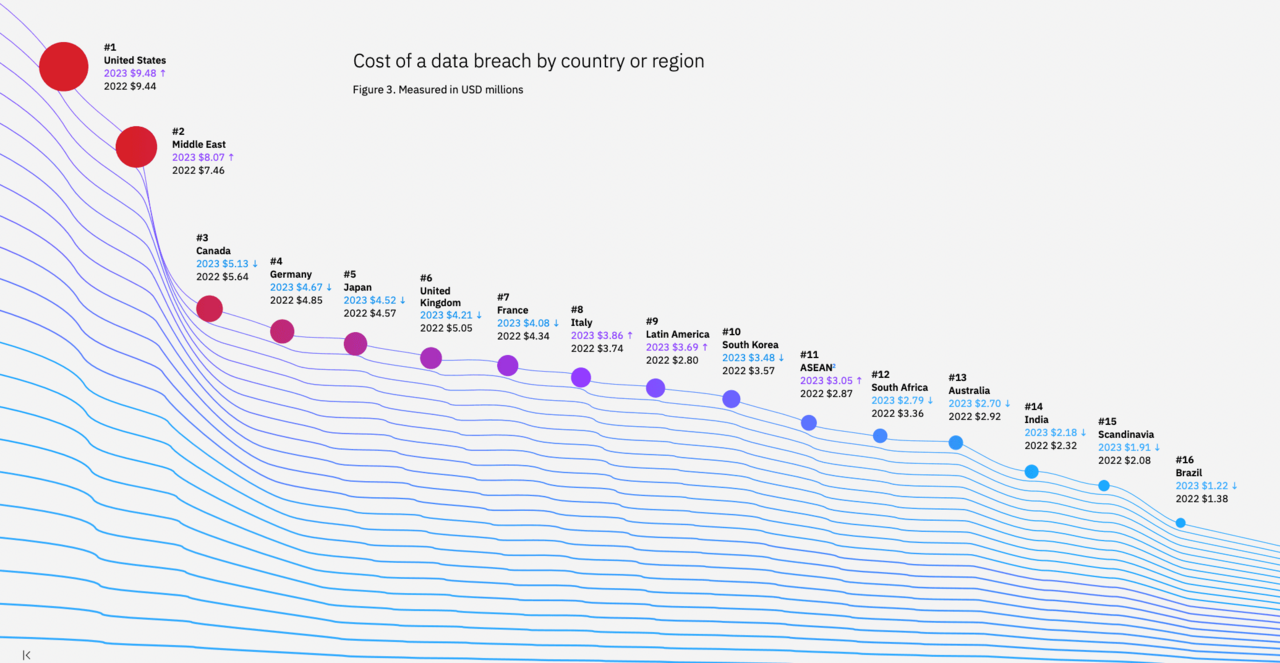
You can also check whether your address appears in known breach collections using a reputable lookup service run by a security researcher or by your browser or password manager.
The first hour of a data breach response
- Change the password on the affected service. Choose a long, unique one. A password manager will generate and store it.
- Change it anywhere else you used the same password. Attackers try leaked passwords on other sites automatically, so reuse is how one breach becomes five.
- Turn on two-factor authentication for the account and for your email, which is the key to resetting everything else.
- Sign out of all sessions if the service offers it, so anyone already logged in is cut off.
- Review account settings. Look for changed email addresses, forwarding rules, new connected apps or added phone numbers.
If financial details were involved
Look over recent statements on cards and bank accounts linked to the service. Report anything unfamiliar to your bank right away. If card numbers were exposed, ask the issuer to replace the card. Consider placing a fraud alert or a credit freeze with the credit reporting agencies where that option exists in your country, as it makes opening accounts in your name harder. Freezes are generally free and can be lifted when you need credit.
If personal identifiers were exposed
Names, birth dates, addresses and national ID numbers can’t be changed like passwords. The defense is vigilance: watch for credit applications you didn’t make, tax filings in your name, or medical bills for care you didn’t receive. Many governments offer identity protection pins for tax filings or similar tools. Keep records of what you do and when, in case you have to dispute something later.
Expect follow-up scams
After a breach, criminals know people are alert and send convincing messages that reference the incident. They might pose as the company, your bank or a law firm offering compensation. Do not click links or open attachments in unexpected messages, and do not give out codes sent to your phone. If you’re unsure, contact the organization via a number or address you already trust.
Prioritize by what an attacker could do with each account. Your main email comes first, since password resets for nearly everything else land there. Next come banking and payment accounts, then work logins, then social profiles and shopping sites. A good data breach response does not try to fix everything at once; it closes the most dangerous doors first. If you manage accounts for family members, such as an older parent, check theirs the same day.
Know your rights too. In many places companies must tell affected people within a set time, and what companies must tell you after a breach covers what a notice should contain. Physical security follows the same logic of limiting damage, as what a high-profile home burglary teaches everyone illustrates. Wikipedia’s entry on data breaches gives a neutral overview.
Long-term data breach response habits
Use the incident to improve your habits. Move to a password manager if you haven’t. Delete old accounts you no longer use, since each one is a place your data can leak from. Use unique email aliases for different services, so a leak points to its source and spam is easy to filter. Consider whether a service really needs your date of birth or phone number, and give less when it doesn’t.
Perspective
Breaches are common enough that a ready data breach response is worth having, and that assuming at least some of your data is already out there is realistic. The aim isn’t perfect privacy. It is to make sure a leak from one place cannot reach the rest of your life. Spend the hour, set up the second factor, and then get on with your day.
Keep a short incident note
Write down the date you heard about the breach, as part of your data breach response, which accounts you changed, and any suspicious messages that followed. If something does go wrong months later, this note saves time when you call a bank or file a dispute. Store it somewhere safe, offline if you like. It also helps you notice if the same service has a second incident, so you can decide whether it deserves your business at all.
A solid data breach response is mostly a matter of order and calm: passwords, second factors, financial checks, then monitoring. Write it down once and you can repeat the same data breach response the next time a notice lands in your inbox.
Image: User:Kowalski7cc / Wikimedia Commons, CC0.



